
ExceedGRC · All-in-one GRC platform
Simplify compliance. Take control of risk.
ExceedGRC brings compliance assessments, risk management, policies, assets and evidence into one dashboard. Built by our own GRC consultants, it replaces spreadsheets and email threads and is designed to be operational within days.
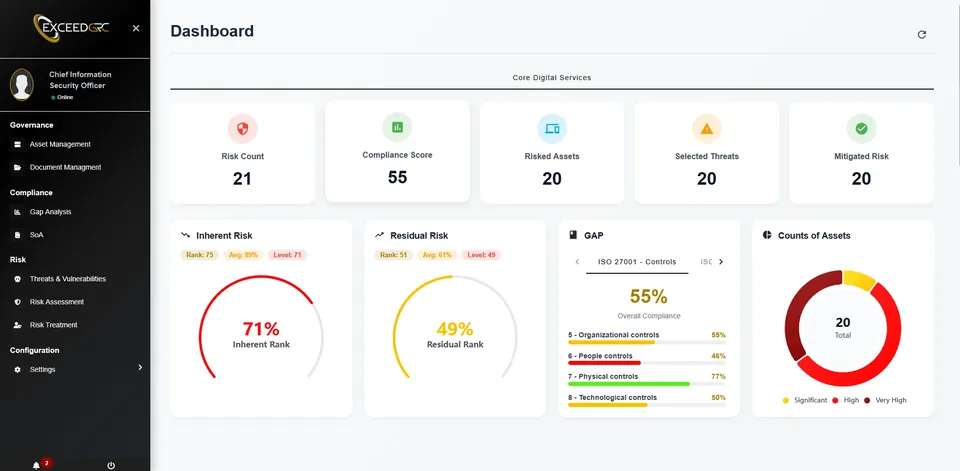
The platform
Compliance, risk, governance. One view of your security posture.
Multi-framework compliance
Assess against multiple frameworks such as ISO 27001, SOC 2, NIST CSF, PCI-DSS, SAMA CSF and NCA ECC, with control maturity scored automatically.
Automated risk management
Risks are calculated from your gaps and vulnerabilities, mapped to threats and assigned to owners, so treatment starts from evidence, not opinion.
Centralised governance
Policies, documents, assets and approvals sit in one governed repository with version control, so the audit trail builds as people work.
How it works
Six steps, with a four-phase cycle at the core.
Onboarding sets up your frameworks and users. From there, ExceedGRC takes your team through governance, risk, compliance and mitigation in one continuous cycle.
Onboarding and go-live
We agree your frameworks, risk criteria and users, then set up ExceedGRC in the cloud or as a VM on your own network.
Governance
Write, review and approve the policies and processes your chosen standards require, each with an owner and a version history.
Risk assessment
Value assets on confidentiality, integrity and availability, map threats and vulnerabilities, and let the platform calculate each risk.
Compliance and gap
Score every control for maturity, upload and validate the evidence, and see your gap to each framework at a glance.
Risk mitigation
Assign treatment tasks to risk owners, send automated reminders and follow every action until the risk is brought down.
Executive reporting
Dashboards show compliance status and risk exposure, and audit-ready reports are ready for your board or your regulator.
Inside the platform
Compliance and risk, documents and assets, workflow and reporting.
Delivered as a configured platform, in the cloud or on-premises, with onboarding for your team. Expected outcomes: compliance and risk managed in one place, less manual effort on evidence, and audit-ready reports for your board and regulator.
01 · Assess
Compliance and risk
Compliance & Gap Assessment module
CMMI-based control maturity scoring
Evidence upload and validation workflow
Risk Management Automation module
Risk calculated from gaps and vulnerabilities
Threat mapping and risk ownership tracking
02 · Govern
Documents and assets
Documentation Management & Lifecycle module
Central repository with version control
Review and approval workflows
Asset Management & Valuation module
CIA-based asset valuation
Assets linked to risks, threats and requirements
03 · Report
Workflow and reporting
Workflow & Collaboration module
Risk owners, tasks and automated notifications
Evidence-based approvals
Dashboards & Reporting module
Compliance status and risk exposure views
Executive and audit-ready reports
Track record
Shaped by GRC projects our consultants deliver.
Financial services · Jordan · 2025
Financial-sector ISMS maintained and recertified to ISO 27001
Tech & digital platforms · Jordan · 2025
ISO 27001 internal audit completed in Q4
IT Security C&T · ISO 27001
We hold ISO 27001 certification for our own ISMS
Test your own framework live in ExceedGRC.
Bring the framework you answer to and a few of your controls. In a live session, a consultant runs a gap assessment in ExceedGRC, shows risks scoring as gaps appear and opens the audit-ready report, so you judge the platform against your own requirements.
Related services
The platform tracks it. Our consultants build it.
ExceedGRC works best with expert work behind it. These services produce the policies, assessments and evidence it tracks.
GRC Platform
How we capture your requirements, configure ExceedGRC and deploy it in the cloud or on your own servers.
View deployment optionsCompliance
Consultants who prepare you for SAMA, NCA, PCI-DSS and CBJ audits, with every finding ready to track in the platform.
Explore complianceInformation Security Management
Consultants who build your ISO 27001 ISMS and prepare it for certification, then keep it current in the platform.
Explore ISO 27001Third-Party Risk Management
Assess suppliers by risk tier, so vendor exposure is understood, owned and treated like any internal risk.
Explore TPRMFAQ
Questions buyers ask before a demo.
What CISOs, risk managers and compliance leads ask us before they book an ExceedGRC demo.
Which frameworks can we assess against?
ExceedGRC supports multiple frameworks, such as ISO 27001, SOC 2, NIST CSF, PCI-DSS, SAMA CSF and NCA ECC. In the demo we confirm coverage for the regulators and standards that apply to you, including regional ones.
How quickly can our team start using it?
ExceedGRC is designed to be operational in days, not months. Once your frameworks, risk criteria and users are configured, your team can start its first gap assessment.
Is it suitable for a smaller organisation?
Yes. ExceedGRC scales from SMEs to large enterprises. Smaller teams use it to replace spreadsheets and shared folders, while larger ones rely on its workflows, risk owners and executive dashboards across departments.
Can we host it on our own infrastructure?
Yes. Choose the cloud-based service or an on-premises virtual machine installed on your network by our engineers and consultants, which suits organisations that need to keep GRC data in-house.
How does it link maturity, risk and evidence?
Each control is scored for maturity using a CMMI-based model and backed by uploaded evidence. Gaps and vulnerabilities feed the risk calculation, and every risk links to its assets, threats, owner and treatment tasks.
Request a demo
Choose your frameworks. We'll demo ExceedGRC on them.
Tell us which frameworks you answer to and the size of your organisation, and we will arrange a live ExceedGRC demo built around your requirements.
Tell us your frameworks and organisation size
We prepare a demo around your requirements
You see ExceedGRC live and receive a proposal